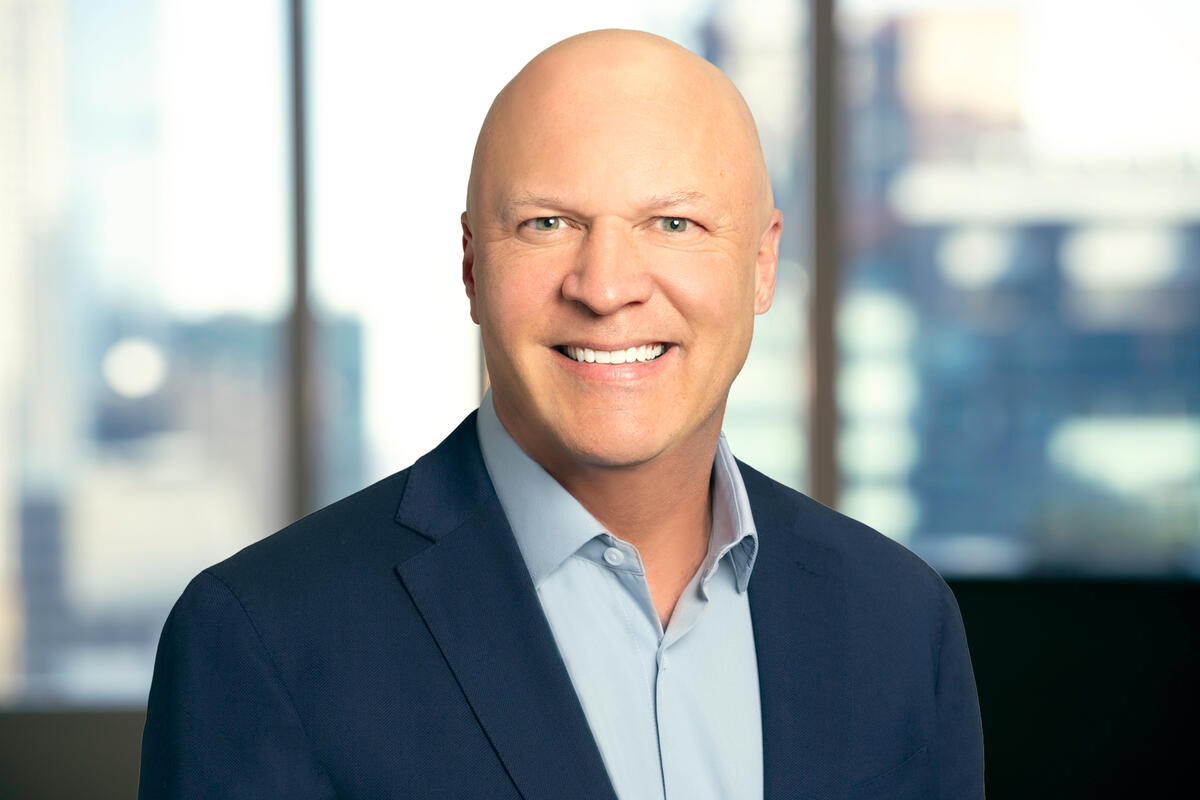
Keith Golden
CIO • INFORMATION TECHNOLOGY & CYBERSECURITY LEADERSHIP • SOUTHERN CALIFORNIAI'm a career CIO who helps companies strengthen their people, processes, and technology to deliver lasting business results—with grounded leadership, thoughtful collaboration, and disciplined execution.
BRIEF BIO
I’m a career CIO.Most recently I led global IT at Resources Global Professionals (RGP), a publicly traded professional services firm — about $500 million in revenue, more than 2,000 users, operations in the U.S., Europe, and Asia. I owned the full stack: applications, infrastructure, cybersecurity, compliance, data, and support.I led IT through a digital transformation that replaced major on-premises platforms with cloud applications and modernized how we worked. We also brought scrum-at-scale agile, with full business ownership, into the legacy enterprise application teams.Cybersecurity has been a big part of my last three roles. I was the de facto CISO at all three, including two public companies — security strategy, incident response, compliance, executive risk reporting, and remediation. I hold a current CISSP credential.Before RGP, I led IT through a turnaround at a $1B publicly traded staffing firm that resulted in a successful sale. Before that, I led IT at an engineering-driven technology company, culminating in a successful ERP transformation.
How I lead
- Understand why I’m needed. What’s working well? What’s not? What does the company need from IT going forward? I work with my executive sponsors to distinguish what needs immediate attention from what needs to happen over time. I clarify where commitments are at risk, what has prevented progress, and the constraints we need to work within. Executive teams often see some of the issues holding IT back, but not all of them. In successive roles, I’ve uncovered problems that had gone unrecognized and led the work to address them. Together, we establish priorities and milestones, with a shared understanding of what I will deliver and how I will be held accountable.- Learn quickly, with an eye for what cannot wait. In my second week in a recent role, a critical infrastructure failure required immediate attention. I led the response and kept the CEO and CFO informed. We kept the business running without revenue or data loss, then strengthened business continuity practices. Cybersecurity gets the same early attention. In two recent roles, audits initiated within my first six weeks exposed previously unknown critical vulnerabilities that we subsequently closed. I take responsibility for understanding these risks early and acting on what we find.- Give difficult decisions the attention they deserve, then act. I give people and partners a fair opportunity to address problems. I also recognize when further delay puts the company at greater risk. During a major transformation, a partner's failure to meet its commitments required a replacement and a revised rollout sequence. We preserved progress while resolving the dependency. I am prepared to change course and take responsibility for the consequences.- Boost the team’s ability to deliver through change. In another role, I inherited a team worn down by repeated reductions, with more difficult changes ahead. Keeping key people engaged required candor, individual attention, and follow-through, even when the outlook was stormy. I give my leaders clear responsibilities and room to make decisions. They need to know where they stand, what is expected, and that I will support them through difficult work.- Build the capability to carry the business forward. I’ve led major transformations that required the IT organization to develop new capabilities while delivering new systems. In my most recent role, we kept the team together through an enterprise transformation and adopted modern software delivery practices. Clear business ownership in tandem with Agile development practices helped critical changes move in days rather than months. I’ve also helped introduce enterprise AI capabilities with governance and targeted business uses. Across these efforts, I establish who owns the outcomes and risks, how decisions are made, and how the organization will operate and support what we introduce.
Where I've Been Accountable
***Major transformation that doesn't interrupt the businessWhen the company needs a major change in its platforms and processes, and how work gets done, the biggest constraint is continuity. Revenue, controls, and customers do not pause just because you're running a transformation. Miss that, and the program itself becomes the risk.I’ve led enterprise transformation programs that replaced fragmented legacy environments and modernized operating methods while the business stayed online.***IT gets smaller, sharper, and ready for a saleIn a turnaround, it's easy to starve IT until something breaks. The better approach is to protect cyber and essential services, cut waste (it's there if you know how to look for it), motivate the core team, and keep the shop exit-ready.I’ve run that through a public-company turnaround that resulted in a successful transaction, and run effective IT optimization efforts in all my CIO roles.***There's no budget for a C-Level Security OfficerMany mid-market firms don't have budget for a CISO, but Boards, auditors, and threat actors don’t care about that. Public-company controls, incident readiness, and day-to-day cyber must operate effectively within IT's constraints.Across my last 3 CIO seats I've owned the combined IT & Cyber remit, with a breach-free record during my tenure at each.***IT Needs Leadership and GovernanceBoards and CEOs need clear ownership of priorities, risk, and investment — not a stack of roadmaps. IT teams need leadership that grows their capabilities through change.I’ve built that operating discipline into how IT runs: steering priorities, investment governance, and accountability for delivery and risk. Enterprise AI sat inside that same frame — guardrails and practical use cases. My teams grow and stick with their mission through difficult transformations.***We just bought a company — now make the tech fitAcquisitions look easy in theory but can get messy in practice. Continuity, identity, apps, and support have to land without a multi-year science project.I've integrated a critical acquisition into a running global IT shop while the core transformation was underway, with no service loss or downtime.
Executive Experience
RGP (NASDAQ: RGP) — CIO
Dec 2022 – Mar 2026 · Public · Professional Services · $500M · Global- Led a 55-person global IT organization and $20M+ in annual technology spend for 2,000+ users — applications, infrastructure and operations, cybersecurity, compliance, budgeting, procurement, and support.- Replaced fragmented legacy apps and manual processes with a set of 5 core ERP/CRM/ATS cloud applications via a successful digital transformation program.- Led cyber with a breach-free record, integrated a keystone acquisition, stood up Scrum@Scale, Agile, modernized infra & network, coached the global IT team through the change, and introduced governance for enterprise AI.
Volt Information Sciences (NYSE: VOLT) — CIO
2021 – 2022 · Public (Taken Private) - Staffing / Professional Services · $1B · Global- Led a 48-person global IT organization and ~$20M in annual technology spend for 1,000+ users across the U.S., Asia, and Europe — applications, PMO, infrastructure, cybersecurity, compliance, and support — through restructuring and a successful sale to ACS/Innova.- Cut IT spend 15% while improving service quality and operating discipline.- Maintained a breach-free record through restructuring and ownership transition, and integrated an MSP into the operating model for infrastructure scale and cost reduction.
Econolite — CIO
2010 – 2021 · Private · Manufacturing/Services · North America- Modernized the IT platform and team, recruited away when the modernization effort was completed.- Replaced legacy on-prem applications with cloud-based ERP & CRM solutions, modernizing finance, operations, sales, and customer processes, preparing Econolite for sale soon afterwards.- Implemented MES and PLM across plants to couple engineering and manufacturing, stood up IT governance for investment prioritization and execution, and matured cyber while the business grew.
Recent Press & Recognition
CIO — High EQ Drives Digital Transformation at RGP
TechTarget — What the 2026 Global Risks Report Means for CIOs
CIO — 5 Business Concepts IT Leaders Should Master
CIO — 7 IT Wins to Deliver Before the Year Ends
WSJ/CIO Journal — IT Unemployment Fell in August. But the Tech Jobs Market Is Still Shrinking.
InformationWeek — Digital Transformation Is a Golden Opportunity for RGP
CIO — CIOs Confront the AI Execution GapSoCal CIO ORBIE Awards — Large Corporate Finalist — 2025
Los Angeles Business Journal / SoCal CIO ORBIE Awards Special Section — Keith Golden, CIO, RGP — October 2025
Keith Golden © 2026 All rights reserved.